Wednesday, October 14

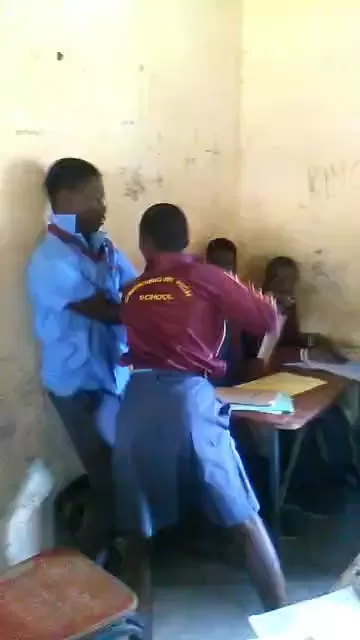
ZRP Sungai Mukomana Uyu Kuponda Musikana

ZRP Sungai Mukomana Uyu Kuponda Musikana

videi Rese WhatsApp https://whatsapp.com/channel/0029Vb6dxKvFCCoXLbB8dA39


  • Share:

Info News

Best Personal Injury Lawyer for Catastrophic Accident Claims

Catastrophic injuries change lives permanently.

A serious brain injury, spinal cord injury, or severe burn accident can create medical expenses that last decades. Families suddenly face lost income, rehabilitation costs, home modifications, and nonstop financial pressure.

That’s why choosing the best personal injury lawyer for catastrophic accident claims matters far more than most people realize.

What Makes Catastrophic Injury Cases Different

These cases involve far more than immediate hospital bills.

Lawyers often evaluate:

  • Long-term medical care
  • Future lost income
  • Permanent disability
  • Rehabilitation expenses
  • Emotional suffering
  • Life-care planning

Settlement values can become extremely high.

Why Insurance Companies Fight Hard

Large injury claims threaten insurance company profits.

That’s why insurers aggressively investigate:

  • Medical history
  • Employment records
  • Surveillance footage
  • Social media activity

Strong documentation becomes critical.

Final Takeaway

Catastrophic injury cases require experienced legal strategy, detailed medical evidence, and long-term financial planning.

The right attorney can help protect victims from accepting settlements that fail to cover future needs.


Best Medical Malpractice Lawyers for Surgical Error Lawsuits

Surgical errors can destroy lives in seconds.

Wrong-site surgery. Anesthesia mistakes. Internal injuries. Delayed diagnosis.

Medical malpractice claims involving surgical negligence are among the most complex legal cases in the healthcare industry.

Why Surgical Error Cases Are Difficult

Hospitals and insurance providers defend these claims aggressively.

Medical malpractice lawyers often work with:

  • Medical experts
  • Surgeons
  • Hospital compliance specialists
  • Economic damage analysts

Evidence matters heavily.

Compensation in Surgical Error Cases

Victims may pursue damages involving:

  • Additional surgeries
  • Lost income
  • Long-term disability
  • Pain and suffering
  • Rehabilitation costs

Severe malpractice cases can result in major settlements.

Final Takeaway

Medical malpractice lawsuits require strong evidence, experienced legal counsel, and detailed medical analysis.

The strongest cases usually combine expert testimony with extensive documentation.

Endpoint Detection and Response vs Antivirus: Business Guide

Traditional antivirus software helped businesses block known malware for many years. But modern attacks often involve stolen passwords, malicious scripts, remote access tools, fileless techniques, ransomware, and attackers who move through a network before launching the final attack. Endpoint detection and response, or EDR, is designed to provide deeper visibility and faster response than basic antivirus.

An endpoint is a device such as a laptop, desktop, server, or virtual machine. EDR software monitors endpoint activity for suspicious behavior. Instead of only checking whether a file matches a known virus signature, EDR can watch processes, command-line activity, network connections, registry changes, file behavior, privilege escalation, and lateral movement.

The key benefit is detection of behavior. For example, if a legitimate tool begins running unusual commands, disabling security settings, dumping credentials, or encrypting many files quickly, EDR may flag that activity even if no traditional virus is detected. This is important because attackers often use normal administrative tools to avoid detection.

EDR also supports investigation. Security teams can review what happened on a device, when it happened, which files were touched, what user account was involved, and whether other machines show similar activity. This timeline can help determine whether an alert is harmless or part of a real incident.

Response features vary by product. Many EDR tools can isolate a device from the network, stop a process, quarantine a file, roll back certain changes, collect forensic data, or trigger automated playbooks. Isolation can be valuable during a ransomware event because it can stop a compromised workstation from reaching shared files or other systems.

Managed detection and response, or MDR, adds human monitoring. Many small businesses do not have a security operations center. MDR providers review alerts, investigate suspicious activity, and help respond. This can be useful because EDR tools can generate alerts that require expertise to interpret.

Antivirus is not useless. Many EDR platforms include antivirus capabilities. The point is that antivirus alone may not provide enough visibility for today's threats. Businesses should think in layers: email security, multifactor authentication, patching, backups, firewall controls, DNS filtering, least privilege, security awareness, and EDR.

When evaluating EDR, ask what operating systems are supported, whether servers are included, how alerts are monitored, whether response is automated or human-led, how long data is retained, and whether reports are available for audits or cyber insurance. Also ask how the tool handles offline devices and remote workers.

Performance matters. Security software that slows machines can frustrate employees and lead to workarounds. Pilot the tool on a small group before full deployment. Include different device types and power users.

Integration is another consideration. EDR may connect with security information and event management systems, ticketing platforms, vulnerability scanners, identity providers, and firewalls. Integration helps correlate alerts across the environment.

Cost depends on the number of endpoints, feature level, retention period, support, and whether monitoring is included. A low-cost tool without monitoring may be fine for a business with internal security staff. A small company without security expertise may need MDR even if it costs more.

EDR is not a magic shield. Attackers can still succeed if passwords are weak, patches are missing, backups are exposed, or users approve malicious logins. But EDR can improve the chance of spotting suspicious behavior before it becomes a full business outage.

For many businesses, the question is no longer whether antivirus is installed. The better question is whether the company can detect and respond when something gets past the first layer. EDR helps answer that question.